Policy templates for SOC 2 and ISO 27001
Meiyam includes 23 security policy templates, each mapped to the SOC 2 criteria and ISO 27001 requirements it addresses. Between them they address every SOC 2 criterion Meiyam tracks, 11 of the 25 ISO 27001 clause requirements and 64 of the 93 Annex A controls.
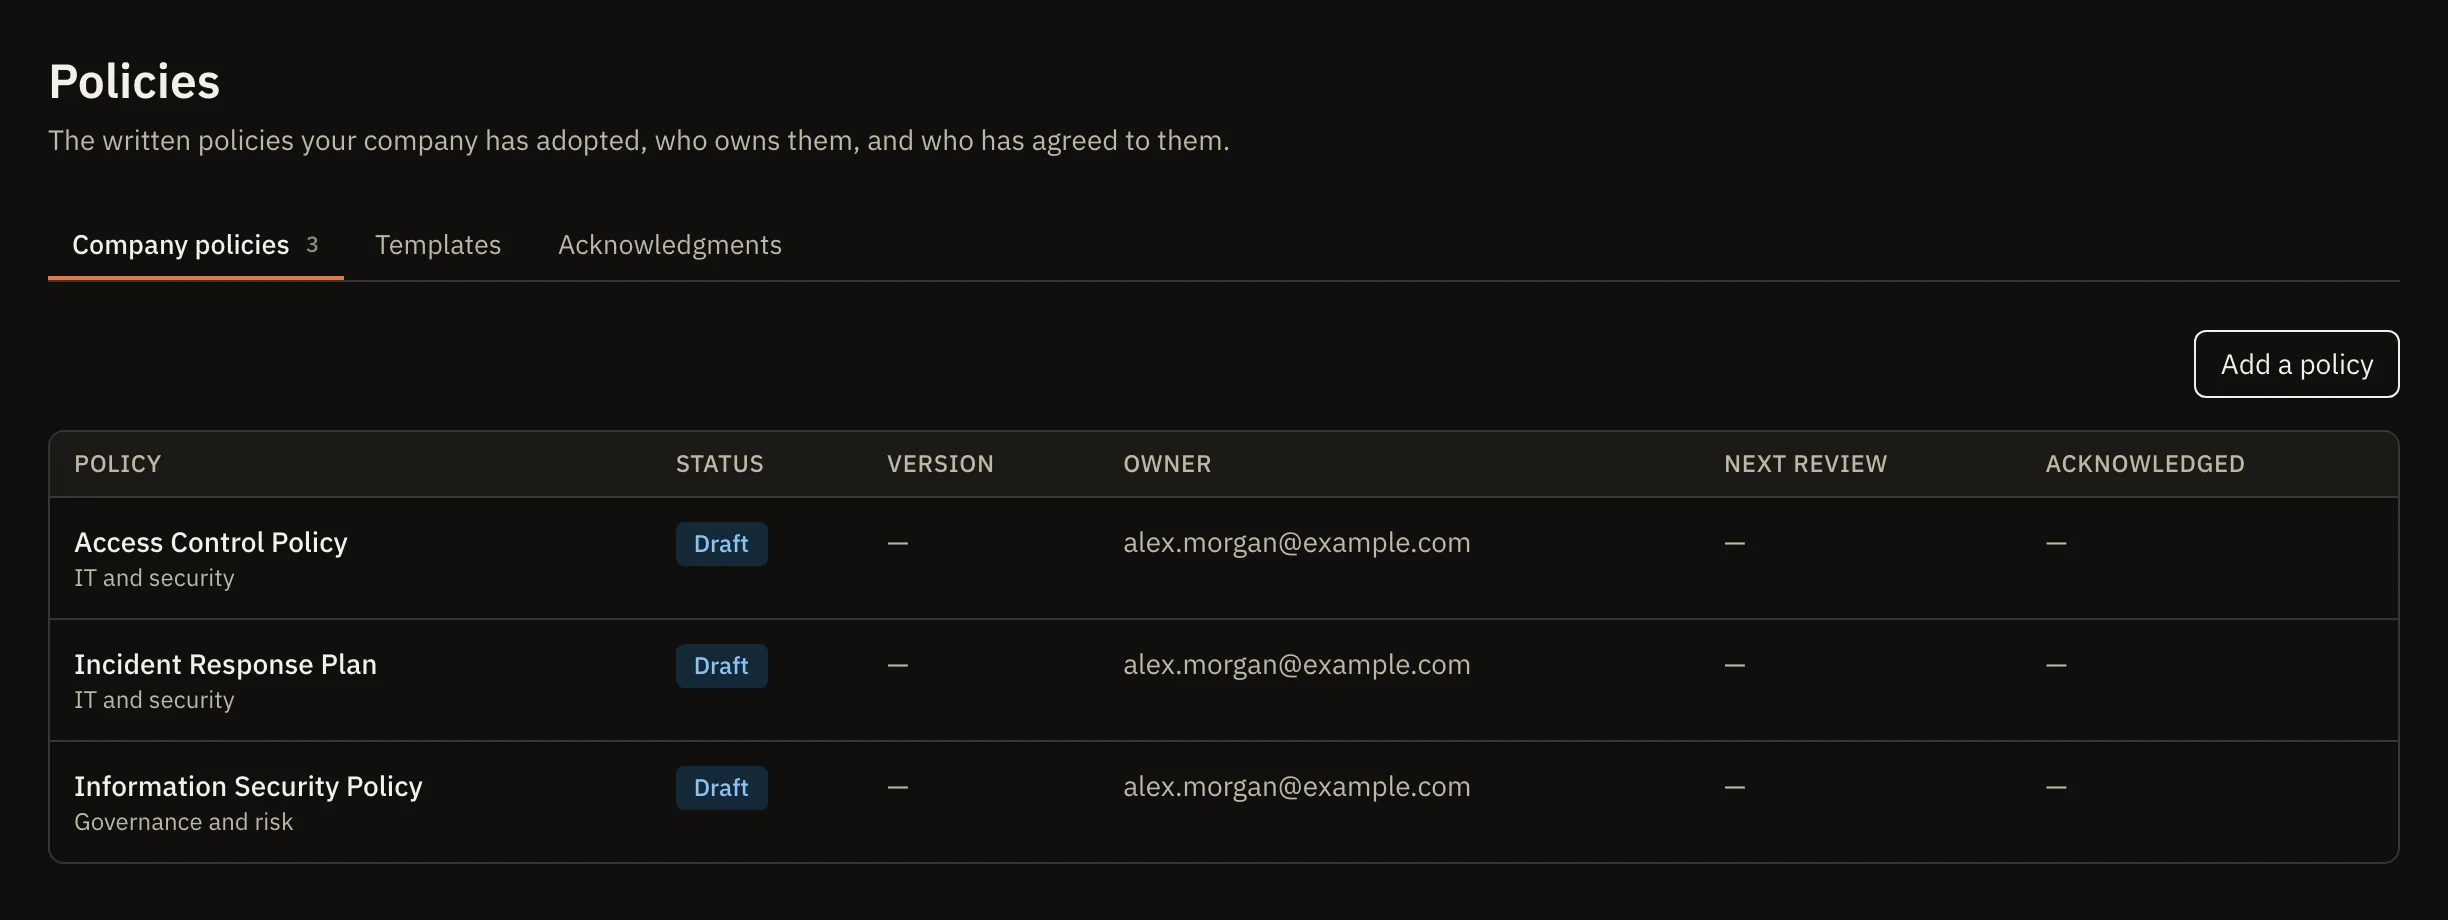
Put a reviewed, approved policy in force
Adopt a template or bring your own policy. Edit it in Meiyam and keep every version. Approving a version puts it in force, and only the workspace owner can approve. Each template comes with an annual review cadence by default, and any version downloads as a Word document.
Included
- Templates mapped to SOC 2 and ISO 27001
- Every version kept
- Owner approval of the version in force
- Annual review cadence by default
- Word download of any version
Know who has accepted each policy
Send each person their own link to read and accept the policies that apply to them. Each acceptance names the policy version it was given for, and the record is exportable for your auditor. Keep the people roster current from a CSV file or by syncing Microsoft Entra ID.
The 23 templates
| Template | SOC 2 criteria | ISO 27001 |
|---|---|---|
| Information Security Policy | CC1.1 to CC1.5, CC2.2, CC2.3, CC3.1, CC5.3 | 5.2, A.5.1 |
| Risk Management Policy | CC3.1 to CC3.4, CC4.1, CC4.2, CC5.1, CC5.2, CC9.1 | 6.1.2, 6.1.3, 8.2, 8.3, 9.1 to 9.3, 10.2 |
| Access Control Policy | CC6.1 to CC6.3 | A.5.15 to A.5.18, A.8.2 to A.8.5 |
| Acceptable Use Policy | CC1.1, CC6.7, CC6.8 | A.5.10 |
| Asset Management Policy | CC6.1, CC6.5 | A.5.9 to A.5.11 |
| Data Classification and Handling Policy | CC6.1, C1.1 | A.5.10, A.5.12, A.5.13 |
| Data Retention and Disposal Policy | CC6.5, C1.2 | A.5.33, A.7.10, A.7.14, A.8.10 |
| Confidentiality Policy | C1.1, C1.2 | A.5.12, A.6.6 |
| Encryption and Key Management Policy | CC6.1, CC6.7 | A.8.24 |
| Network Security Policy | CC6.6, CC6.7 | A.8.20 to A.8.22 |
| Endpoint and Workstation Security Policy | CC6.7, CC6.8 | A.7.9, A.8.1, A.8.7, A.8.9 |
| Logging and Monitoring Policy | CC2.1, CC7.2 | A.8.15 to A.8.17 |
| Vulnerability and Patch Management Policy | CC7.1 | A.8.8 |
| Change Management Policy | CC8.1 | A.8.32 |
| Secure Software Development Policy | CC8.1 | A.8.25 to A.8.29, A.8.31 |
| Vendor and Third-Party Risk Management Policy | CC9.2 | A.5.19 to A.5.23 |
| Personnel Security Policy | CC1.4, CC1.5, CC6.2, CC6.3 | A.6.1, A.6.2, A.6.4 to A.6.6 |
| Code of Conduct | CC1.1, CC1.5, CC2.2 | A.6.2, A.6.4 |
| Security Awareness and Training Policy | CC1.4, CC2.2 | 7.2, 7.3, A.6.3 |
| Incident Response Plan | CC7.3 to CC7.5 | A.5.24 to A.5.28 |
| Business Continuity and Disaster Recovery Plan | CC9.1, A1.1 to A1.3 | A.5.29, A.5.30, A.8.14 |
| Backup Policy | CC7.5, A1.2 | A.8.13 |
| Physical Security Policy | CC6.4, CC6.5 | A.7.1 to A.7.4, A.7.6 to A.7.8 |
Policy questions
Does Meiyam provide SOC 2 policy templates?
Yes. Meiyam includes 23 security policy templates, each mapped to SOC 2 and ISO 27001, that you edit, version and approve in your workspace. Between them they address every SOC 2 criterion Meiyam tracks.
Does a policy template make a control pass in Meiyam?
No. A template is a starting point. A control rests on a policy only once you approve a version and put it in force, and for a Type 2 period you also attach the records that show the control operated. Whether the control is met is your auditor's judgement.
Can I use my own policies in Meiyam?
Yes. Bring your own policy instead of adopting a template, then edit, version, approve and track acceptance the same way.
Start from 23 policy templates
When Meiyam opens, every account starts on a free trial.