ISO 27001 compliance automation, with evidence you can verify
ISO/IEC 27001:2022 sets the requirements for an information security management system: clauses 4 to 10 and the 93 controls of Annex A. Meiyam tracks every clause and control. Automated rules check 18 Annex A controls on every scan, and approved policies and dated records evidence the clauses and the other controls. Evidence is sealed as it is collected, so you can show your certification body it has not changed since.
ISO 27001 Annex A controls
18 of 93
checked by automated rules
- Automated rules 18
- Documents 75
ISO 27001 at a glance
The figures behind Meiyam's ISO 27001 coverage, read from the product's catalogue, rules and policy templates.
- Automated rules, run on every scan. The same rules check SOC 2.
- 77
- Each maps to one Annex A control
- Annex A controls tracked, alongside clauses 4 to 10.
- 93
- Every one starts unproven
- Annex A controls at least one policy template maps to.
- 64
- Out of the 93 in Annex A
- Policy templates, each mapped to ISO 27001 and SOC 2.
- 23
- Every version kept, with owner approval
ISO 27001 in brief
ISO/IEC 27001 sets out how to run an information security management system, and an accredited certification body, not Meiyam, certifies it.
ISO/IEC 27001:2022 is the international standard for an information security management system. Clauses 4 to 10 set out how the system is run: its context and scope, leadership, planning for risk, support, operation, performance evaluation and improvement.
Annex A lists 93 controls in four themes: organisational, people, physical and technological. Your Statement of Applicability records which of them apply to you, and why.
Certification is granted by an accredited certification body after a two-stage audit, and kept through surveillance audits. Meiyam does not certify and does not replace the audit. It keeps the evidence current and shows which clauses and controls still need your input.
| Clauses 4 to 10 | Annex A | |
|---|---|---|
| What they cover | How the management system is run | The controls you apply to treat risk |
| Tracked in Meiyam | Every clause, as 25 requirements | All 93 controls, in four themes |
| Evidenced by | Policies and records | Automated rules for 18 controls, documents for the rest |
| Mapped by policy templates | 11 of 25 | 64 of 93 |
Annex A coverage
Automated rules check 18 of the 93 Annex A controls; documents evidence the rest and every clause.
ISO 27001 requirements by evidence
Automated rules, 18: A.5.14 (3 rules), A.5.17 (2 rules), A.5.18 (6 rules), A.5.23 (3 rules), A.5.33 (2 rules), A.8.2 (5 rules), A.8.3 (4 rules), A.8.4 (2 rules), A.8.5 (16 rules), A.8.8 (2 rules), A.8.9 (4 rules), A.8.15 (7 rules), A.8.20 (3 rules), A.8.21 (1 rule), A.8.22 (1 rule), A.8.24 (7 rules), A.8.28 (3 rules), A.8.32 (6 rules).
Controls evidenced by documents
A.5.1, A.5.2, A.5.3, A.5.4, A.5.5, A.5.6, A.5.7, A.5.8, A.5.9, A.5.10, A.5.11, A.5.12, A.5.13, A.5.15, A.5.16, A.5.19, A.5.20, A.5.21, A.5.22, A.5.24, A.5.25, A.5.26, A.5.27, A.5.28, A.5.29, A.5.30, A.5.31, A.5.32, A.5.34, A.5.35, A.5.36, A.5.37, A.6.1, A.6.2, A.6.3, A.6.4, A.6.5, A.6.6, A.6.7, A.6.8, A.7.1, A.7.2, A.7.3, A.7.4, A.7.5, A.7.6, A.7.7, A.7.8, A.7.9, A.7.10, A.7.11, A.7.12, A.7.13, A.7.14, A.8.1, A.8.6, A.8.7, A.8.10, A.8.11, A.8.12, A.8.13, A.8.14, A.8.16, A.8.17, A.8.18, A.8.19, A.8.23, A.8.25, A.8.26, A.8.27, A.8.29, A.8.30, A.8.31, A.8.33, A.8.34, 4.1, 4.2, 4.3, 4.4, 5.1, 5.2, 5.3, 6.1.1, 6.1.2, 6.1.3, 6.2, 6.3, 7.1, 7.2, 7.3, 7.4, 7.5, 8.1, 8.2, 8.3, 9.1, 9.2, 9.3, 10.1, 10.2.
Automated rules cover 13 technological and 5 organisational controls. People and physical controls, and the clauses, are evidenced by documents.
Example rules for each Annex A control
| Control | Example rules |
|---|---|
| A.5.14 |
|
| A.5.17 |
|
| A.5.18 |
|
| A.5.23 |
|
| A.5.33 |
|
| A.8.2 |
|
| A.8.3 |
|
| A.8.4 |
|
| A.8.5 |
|
| A.8.8 |
|
| A.8.9 |
|
| A.8.15 |
|
| A.8.20 |
|
| A.8.21 |
|
| A.8.22 |
|
| A.8.24 |
|
| A.8.28 |
|
| A.8.32 |
|
Clauses and documents
The management-system clauses and the organisational, people and physical controls are evidenced by policies and records, each with a freshness threshold.
The clauses and most organisational, people and physical controls describe how you run security, so documents evidence them. Meiyam's 23 policy templates map to 11 of the 25 clause requirements and 64 of the 93 Annex A controls.
Some clauses need records rather than policies. For risk assessment and risk treatment (clauses 6.1.2 and 6.1.3), attach your risk assessment and risk treatment plan as documents; the Risk Management Policy template sets out how you run them. A risk register in Meiyam is planned.
Meiyam does not generate a Statement of Applicability. Write your own and attach it to clause 6.1.3 as a dated document, like any other record.
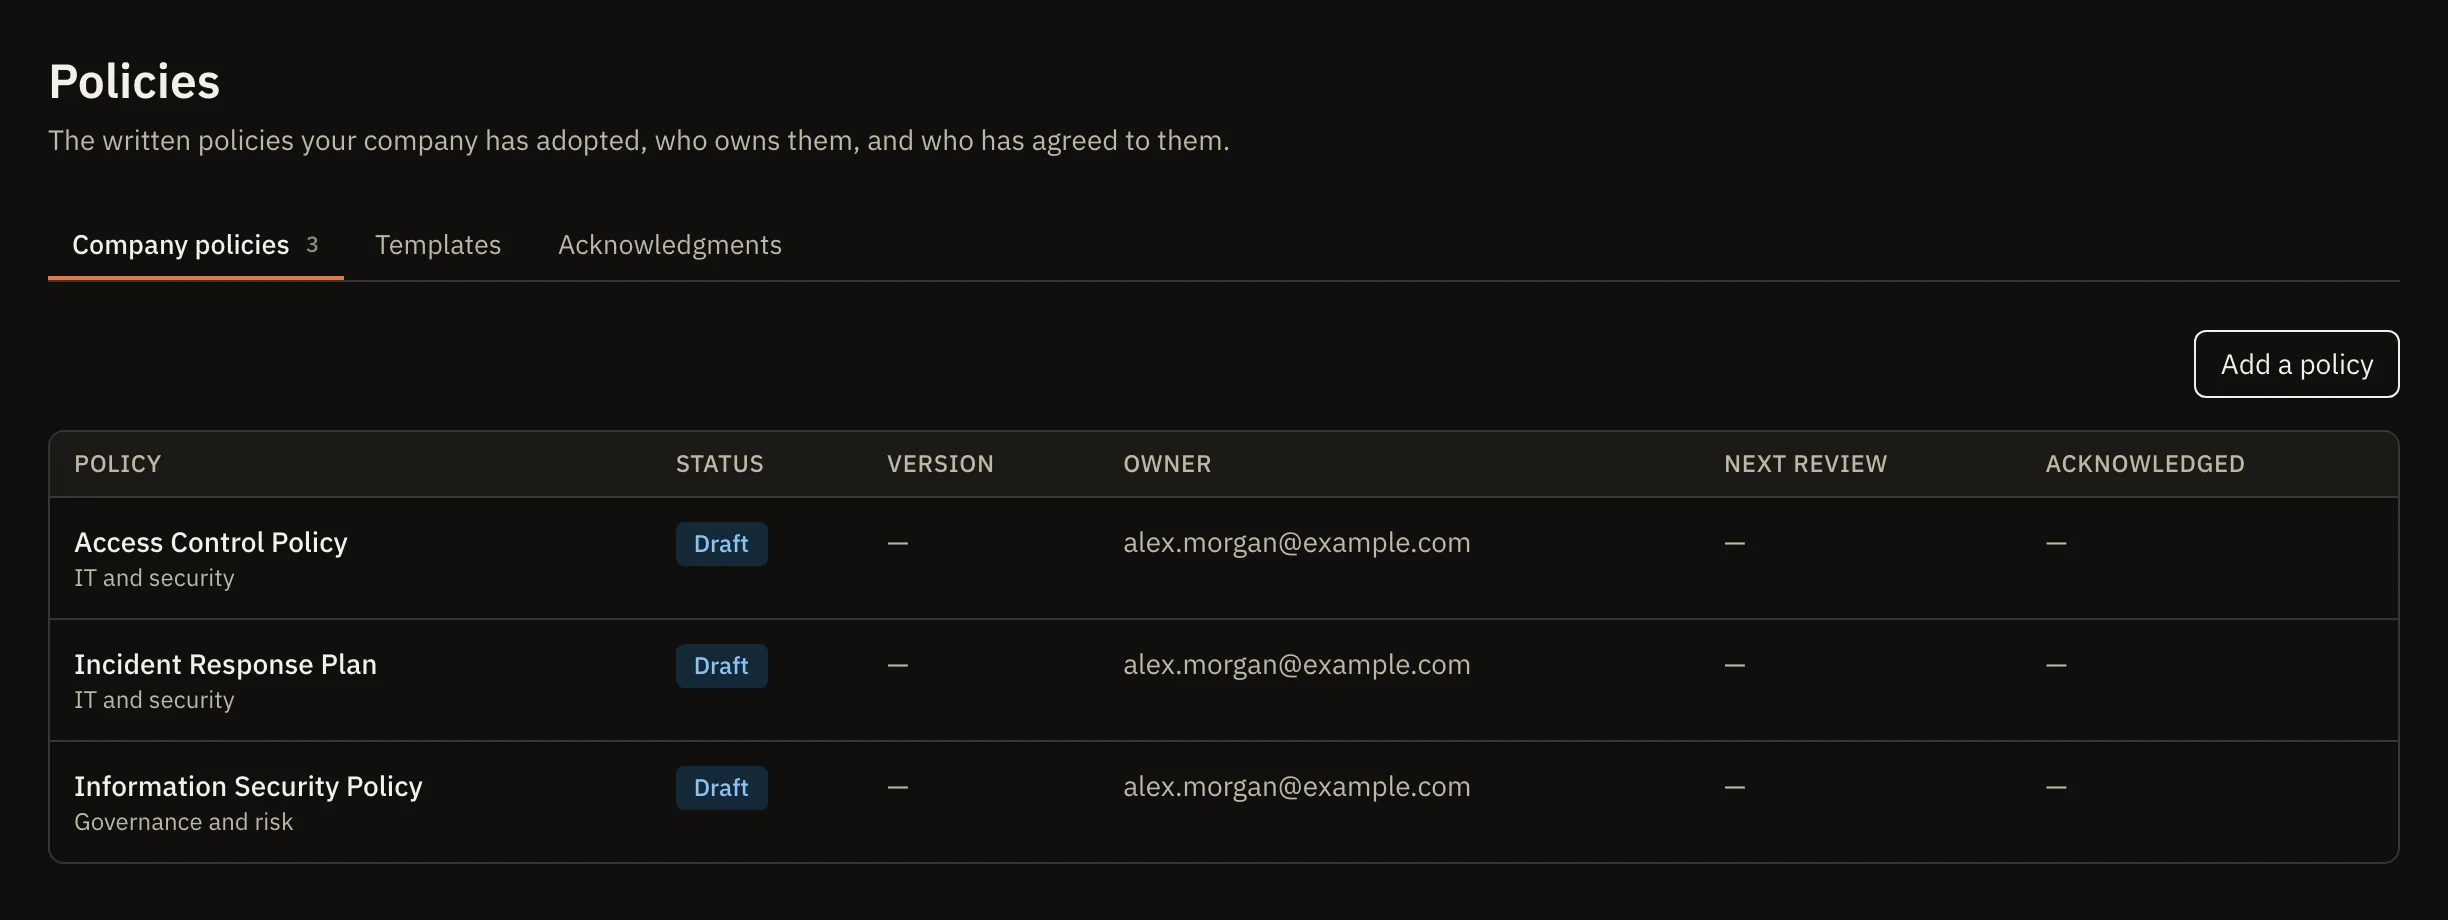
Approve a policy version to put it in force, track each person's acceptance, and attach dated records, such as an internal audit report or management review minutes, to the clauses and controls they evidence. A document past your freshness threshold reads as stale.
ISO 27001 questions
Answers to the questions teams ask most when they prepare for ISO 27001 with Meiyam.
Does Meiyam support ISO 27001?
Yes. Meiyam supports ISO/IEC 27001:2022: clauses 4 to 10 and all 93 Annex A controls. Automated rules check 18 Annex A controls on every scan; approved policies and dated records evidence the clauses and the other controls. You write your Statement of Applicability and attach it, and Meiyam shows when it needs renewing.
Does Meiyam produce a Statement of Applicability?
No. Write your own, attach it to clause 6.1.3 as a dated document, and Meiyam tracks its freshness like any other document. None of the 23 policy templates is a Statement of Applicability.
How does Meiyam describe the Annex A controls?
By number, with Meiyam's own short descriptions; the standard's text is not reproduced.
Does Meiyam certify my management system?
No. Certification is granted by an accredited certification body after it audits your management system. Meiyam does not issue certifications or audit opinions, and it does not replace the audit. It organises the evidence the audit relies on.
AM DevOps does not hold an ISO 27001 certification for Meiyam today.
Which version of ISO 27001 does Meiyam track?
ISO/IEC 27001:2022, the current edition: the management-system clauses 4 to 10 and the 93 Annex A controls in four themes. Meiyam does not track the 2013 edition, whose Annex A is structured differently.
Why are only 18 of the 93 Annex A controls automated?
Automated rules cover the controls that configuration can prove. A passing configuration check cannot show that a risk assessment was performed, a supplier was assessed or staff were trained, so those controls are evidenced by documents. Where several rules apply to one control, all of them must pass before the control shows as passing.
Can I run ISO 27001 alongside SOC 2 in Meiyam?
Yes. Both frameworks are scored from the same scans, and every policy template maps to both. One failing check is one finding, counted against the SOC 2 criterion and the Annex A control it affects.
Where is my data stored?
On AWS in the EU (Ireland) region, where scan results, findings and evidence are stored and processed. Each workspace is isolated from every other workspace at the database level, and evidence objects are stored under a path unique to your workspace. The security page has the detail.
Prepare for ISO 27001 certification with evidence you can verify
When Meiyam opens, every account starts on a free trial.